Where Does Technology Sit in the Fight Against Fraud? A Recap From the 4th Annual Asia Anti-Fraud Leaders' Summit 2026
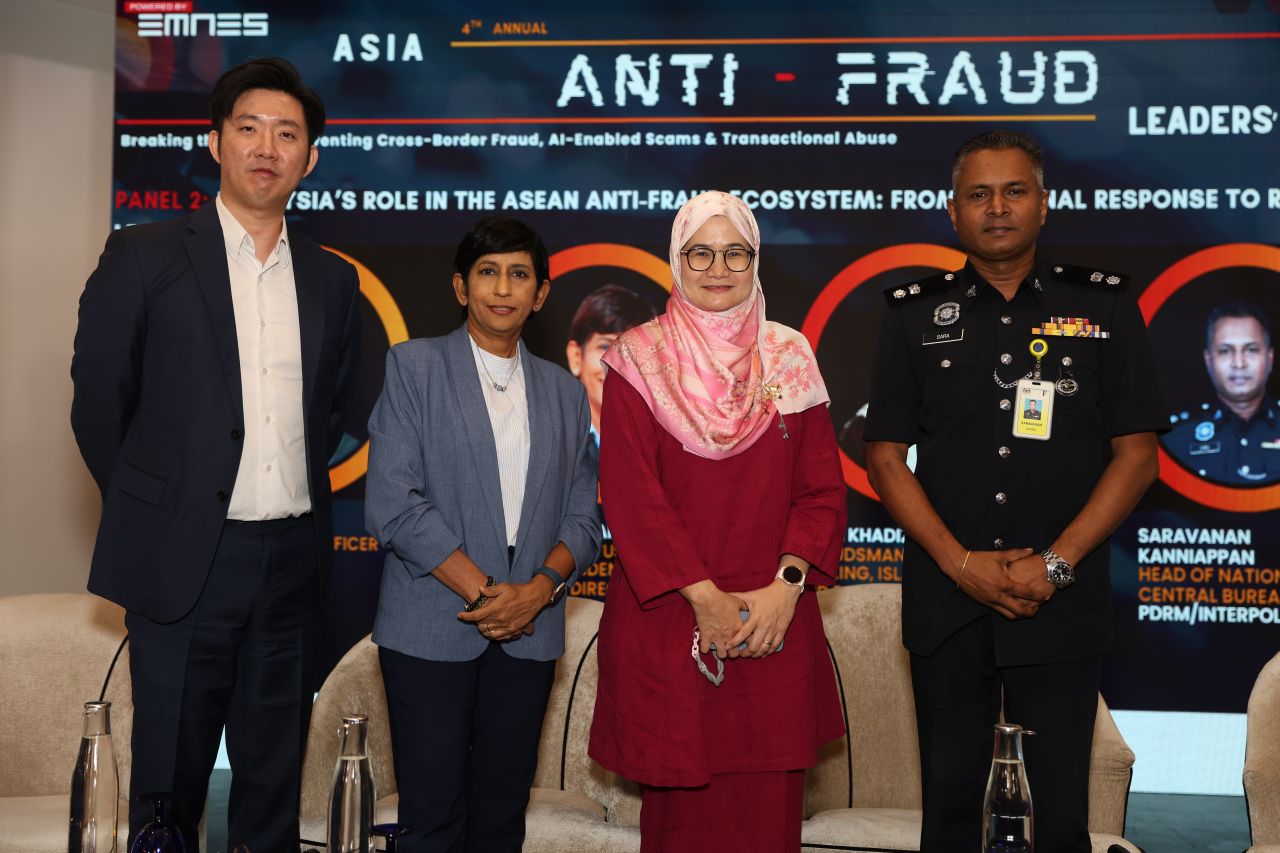
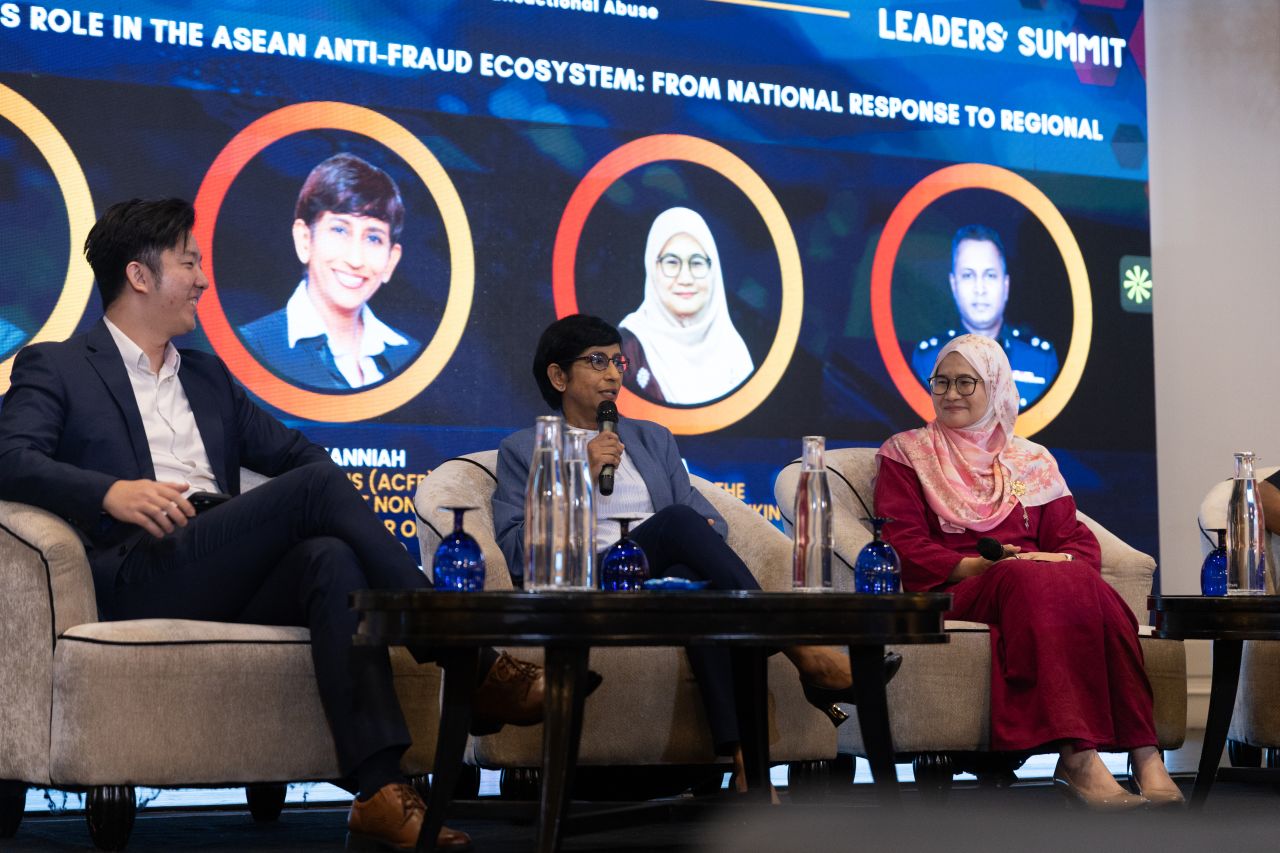
At the 4th Annual Asia Anti-Fraud Leaders' Summit, a panel on Malaysia's role in the ASEAN Anti-Fraud Ecosystem brought together four types of decision makers who rarely share a stage: a technology provider, an industry practitioner, a regulator, and an enforcer.
Four Seats, One Ecosystem
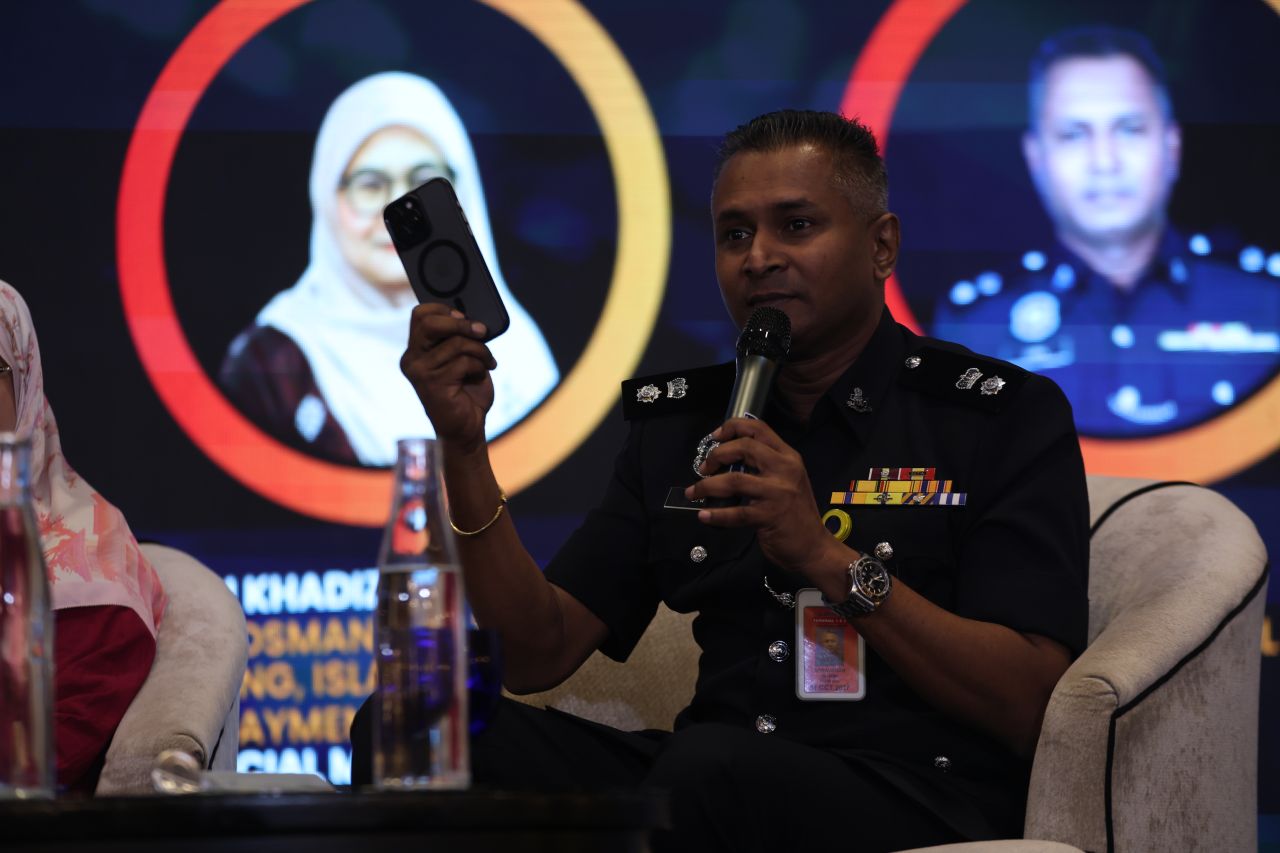
Frederick Chung, CEO of Level Five Group, represented the technology industry alongside Maheswari Kanniah (Regent Emeritus at ACFE), Intan Khadiza (Ombudsman at the Financial Markets Ombudsman Service), and Saravanan Kanniappan (Head of the National Central Bureau at the Royal Malaysia Police / Interpol).
Mature Processes, Fragmented Coordination
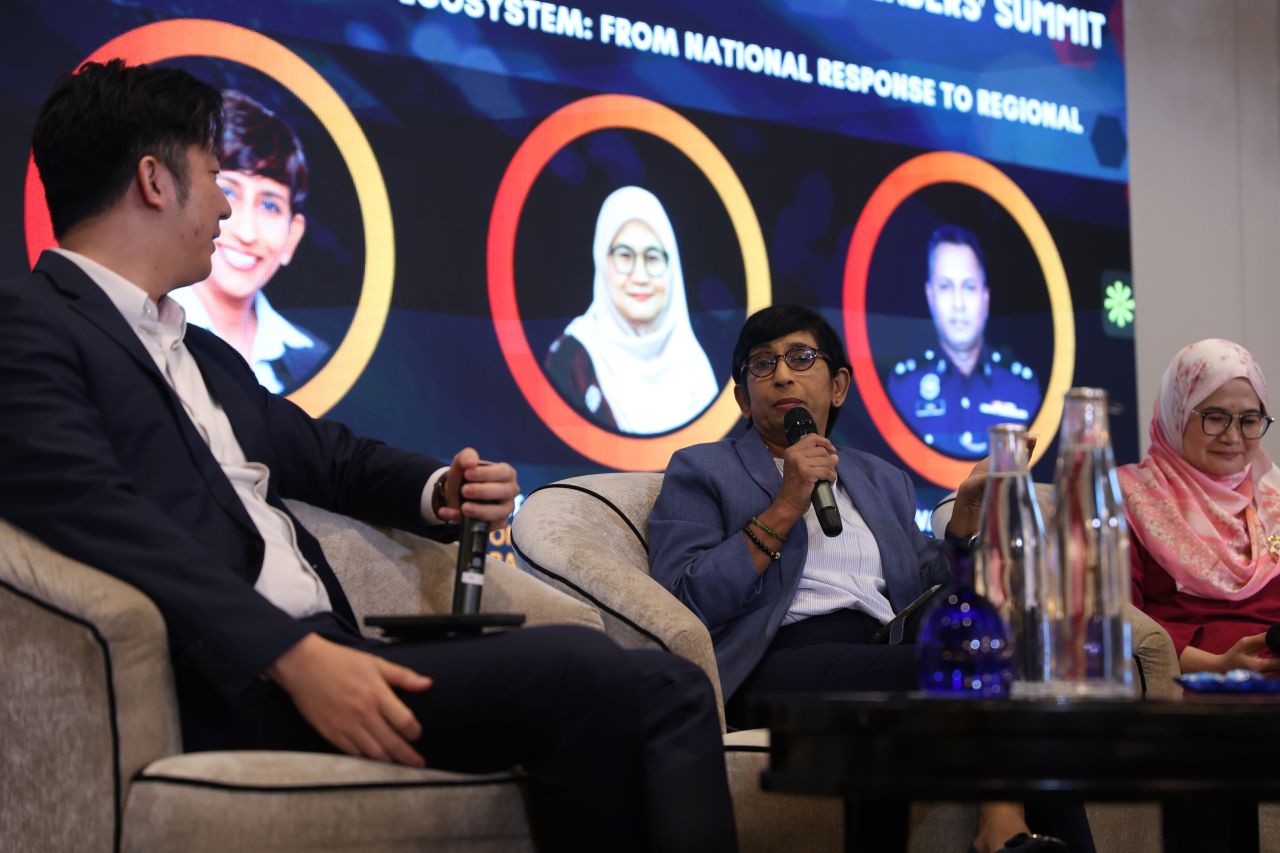
The discussion moved quickly from the polite to the pointed. Bankers and regulators in the room engaged on the gaps between detection and reimbursement, and it became clear the industry's processes are more mature than its coordination. Chung's assessment: the flow from detection to reimbursement is largely robust on paper, but structural issues in current regulations keep that flow from working as one system. Each party operates within its own mandate, and those mandates were not designed to move at the same speed.
Different Mandates, Same Enemy
That mismatch shaped the panel's central tension. Financial institutions answer to profit. Regulators answer to national interest. Enforcers answer to the laws of their jurisdiction. None of these objectives are wrong, but none of them automatically align either. Getting four parties with four different mandates to move in the same direction takes more than a shared enemy in fraudsters. It takes structures built for coordination, not just detection.
What Carries More Weight: Tech or Regulations?
Fred closed the session with a question the room hadn't fully answered: where does technology actually sit in this picture? Most of the conversation around anti-fraud gravitates toward process and regulation, tightening reporting requirements, defining liability, formalising reimbursement timelines. Technology adoption gets treated as a compliance outcome rather than something worth incentivising directly.
His suggestion was a shift in posture. Instead of penalising institutions that fall behind on fraud detection capability, what if the incentive ran the other way? A national-level carrot for early adopters of better anti-fraud systems, rather than a stick for the laggards. It's a simple reframe, but it puts technology providers, financial institutions, and regulators on the same side of an incentive structure instead of opposite sides of an enforcement one.
Knowing the Misalignment is Half the Battle
The value in a panel like this is that the disagreement stays visible instead of getting smoothed over in the summary slide afterward. Regulation alone hasn't closed the coordination gap so far, and another framework by itself probably won't either. What moved the discussion forward was tech, industry, regulators, and enforcement sitting across from each other and naming where their incentives actually pull apart.
Credit to the team at Emnes Events for putting the room together in the first place.
Excited to learn more?
the Future of Secure, Compliant, and Connected Enterprises


