What RUSI’s Toolkit Reveals on Who Owns Fraud
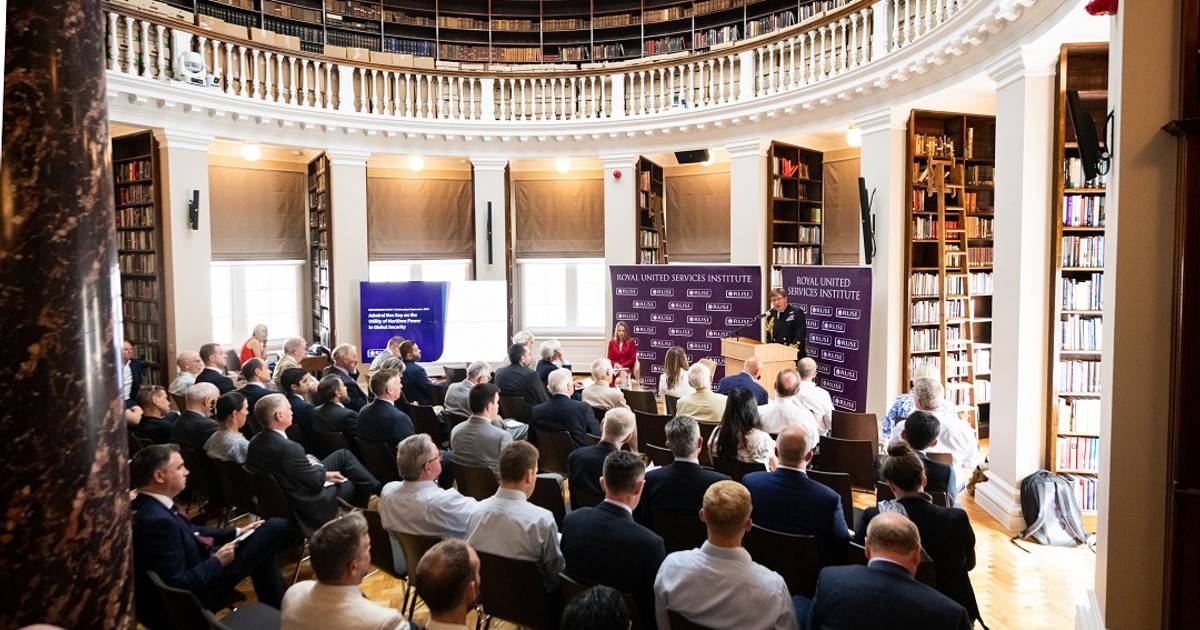
RUSI's new guide on authorised payment fraud policy makes a point worth taking seriously: coordinated national strategies work better than fragmented ones, and the countries getting this right: Singapore, Australia, Malaysia among them, share a common feature. Someone at the top has been named the political owner of the problem: a firm, a central bank, a president's office. Fraud stops being everyone's vague responsibility and becomes one office's explicit mandate.
The report is right to hold it up. But it's also only half the problem solved.
Taking Accountability
Naming a political owner answers the question of who is accountable for fraud at the level of a country. It doesn't answer the same question at the level of an institution.
A national strategy can specify that the Ministry of Home Affairs owns Singapore's response, or that Malaysia's National Fraud Portal coordinates the data, and a bank sitting inside that system can still have no clear answer to a much smaller but more immediate question: when a suspected scam payment lands in their queue right now, who has the authority to act on it before the money moves again?
This is the same gap that shows up whenever a national framework meets an individual institution's org chart. The framework assumes that once accountability exists somewhere, it flows down to wherever the actual transaction is sitting.
In practice, the flow gets interrupted at every layer it passes through. A national anti-scam centre can trace funds across the financial system in real time, exactly as the report describes, and the receiving bank can still take two days to freeze the account, because tracing the funds and having someone with the authority to act on that trace are two different capabilities, built by two different parts of the response.
Working Examples
Malaysia's own National Fraud Portal is a useful illustration of both sides of this. Defining a common taxonomy before launch, in 2023, was the right sequencing, and it's part of why the portal has been able to coordinate data across banks, telcos, and enforcement in a way most jurisdictions still can't.
But a shared taxonomy and a shared portal only solve the industry-level coordination problem. They don't tell an individual compliance officer whether they have standing authority to freeze a flagged account without waiting for sign-off from someone two levels up, at 11pm on a Friday, when the fraud is moving in real time and the institutional decision-making hasn't caught up to the national one.
What Does This Mean for Your Organization?
Most institutions inside a national anti-scam framework can name the framework. Few can say how long it actually takes them to move from a flagged signal to a frozen account, broken down by case type and shift. That number is measurable, and rarely tracked.
Connect with us to map it: here.
Should Responsibility Be Delegated?
The report's five-point framework: establishing the fraud landscape, naming a political owner, setting objectives, defining scope, and engaging delivery partners, is sound as a country-level design. What it doesn't fully reach is the sixth question that determines whether any of it works in practice: once an institution is named a delivery partner, does someone inside that institution actually have the authority to move at the speed the national strategy assumes.
Financial institutions operating in markets with strong national frameworks shouldn't read that as a license to relax. A well-designed portal or anti-scam centre raises the ceiling on what's possible: a chain of authority that can act on a fraud signal in minutes, not days, regardless of how good the national coordination above it looks on paper.
The USD 442 billion in losses the report cites for 2025 didn't happen because countries lacked strategies. Several of the jurisdictions in this study have strategies that are genuinely well designed. The losses happened because a strategy existing at the national level and a decision being made at the institutional level, in time, are not the same event, and the gap between them is where most of that money actually moved.
Measuring Response Times (Level Five's Perspective)
Most of what we see across the region isn't a shortage of national coordination. It's institutions that can point to the national framework they belong to, and still can't tell you how long it actually takes them to act once a fraud signal comes in.
The portal traces the funds and flags the account. What happens between that flag landing and someone inside the institution actually freezing the transfer is rarely measured at all, which means it's rarely improved either.
That gap is measurable, and treating it as a soft, cultural problem, "our teams need better training" or "we need clearer escalation paths", tends to let it go unmeasured indefinitely. The more useful question is a number: from the moment a signal is flagged, how long until action, broken down by case type, by shift, by which team is on the queue. Institutions that can answer that question with data are the ones actually closing the gap the national strategy assumes is already closed. Institutions that can't are relying on the framework above them to do work it was never built to do.
The strategies RUSI documents are worth adopting. However, the distance between a well-designed national system and a fast institutional response is exactly where we spend most of our time, because it's the part no policy document can measure from the outside.
Excited to learn more?
the Future of Secure, Compliant, and Connected Enterprises
