One IP Address, Seven Financial Firms: What Korea's Breach Cluster Actually Shows
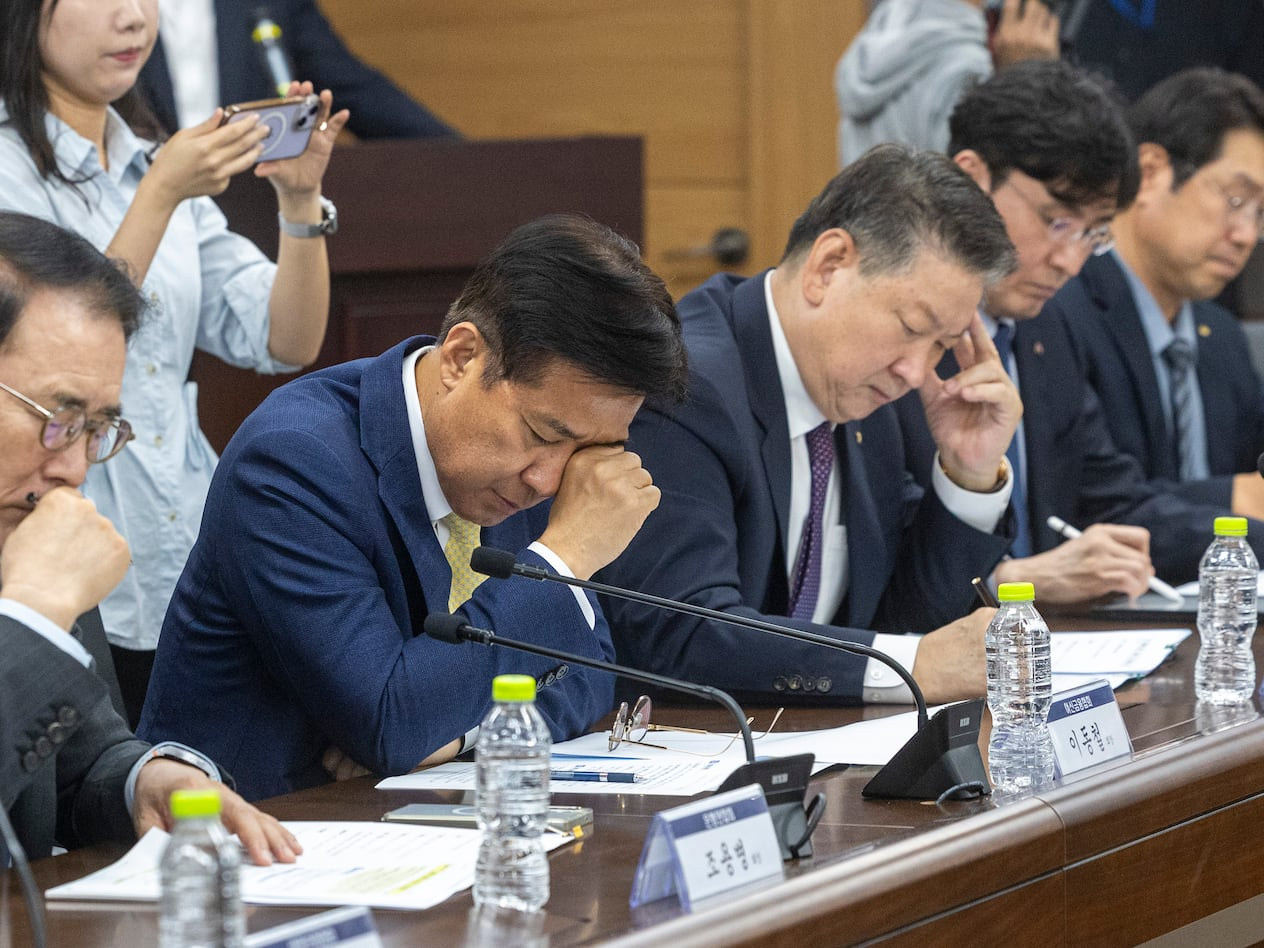
Korean regulators confirmed this week that the same attacker IP address surfaced in breaches at seven financial firms: Shinhan Bank, KB Kookmin Bank, Hana Bank, BNK Busan Bank, Yegaram Savings Bank, Welcome Savings Bank, and Hyundai Capital.
The attackers rotated IP addresses through Korea, the US, Japan, Hong Kong, Singapore, Vietnam, Thailand, and the UK to sustain the campaign. A string found in the HTML title of a compromised web server, written in Chinese, pointed analysts toward an autonomous AI-driven penetration testing tool as the likely method.
No customer-facing banking services were affected. No financial losses have been reported. What was breached sat one layer back: auxiliary systems used by employees and loan brokers, information inquiry services missing identity verification, and web vulnerabilities that had gone unpatched.
The Financial Services Commission has now given banks and card companies until 6 October, and securities firms, insurers, savings banks, and electronic financial service providers until 8 October, to complete emergency security reviews.
The Signal Was There Before the Pattern Was Recognized
A shared IP address across seven separate incidents is, on its own, a thin piece of evidence. It doesn't establish who's behind an attack, and regulators were careful to note that the method, not just the IP, differed between the banking sector and the savings bank sector. But the fact that it took a cross-institutional comparison to surface the pattern at all is the most crucial aspect.
Each of those seven breaches, examined individually, would have looked like a contained incident: a vulnerable service here, an unpatched endpoint there. It was only once someone compared notes across institutions that a single campaign, run by one actor rotating infrastructure to look like separate, unrelated attacks, became visible.
That's the entire logic of this kind of attack. Spread activity across enough targets and enough IP ranges, and each individual institution's security team sees only its own slice of the picture.
AI Didn't Invent This Attack Pattern, It Just Made It Faster
Distributed, rotating attacks against multiple institutions aren't new. What's changed is the volume one actor can now generate without proportionally more people behind it.
An autonomous penetration testing tool, run against hundreds of financial firms, doesn't need the operator to manually probe each target. It tests, adapts, and moves to the next target largely on its own, which is exactly why regulators are treating this less as seven incidents to clean up individually and more as a signal that the underlying security framework needs rebuilding.
That shift in attacker capability has an uncomfortable implication for defenders. A security team built around responding to one incident at a time, however well-resourced, is structured to answer a question this kind of campaign doesn't actually ask.
The relevant question isn't "was this specific endpoint compromised." It's "is this the fourth time this month a familiar pattern has shown up somewhere in the sector," and that question only has an answer if someone is actually looking across institutions, not just within one.
What Does This Mean for Your Organization?
Most financial institutions can tell you whether their own systems were breached. Fewer can tell you whether an attacker signal that touched them also touched three other institutions in the same week, because that comparison depends on visibility none of them have on their own.
Contact us here to talk through what connected threat visibility looks like for your institution.
Cybersecurity and Fraud Need to Align as a Priority, Not a Luxury
The breaches themselves sat in a space that sits awkwardly between two functions: not quite a customer-facing fraud event, not quite a conventional data breach, but an infiltration of employee-facing systems that, if left there, often becomes the staging ground for fraud that does eventually reach customers.
Stolen loan broker credentials and corporate representative data don't stay interesting to an attacker in isolation. They're frequently the raw material for the next stage of the attack, account takeover, synthetic loan applications, social engineering built on real internal data.
Institutions that treat cybersecurity and fraud as two departments with two different reporting lines are structurally slower to see that connection. A cyber team watching for intrusion and a fraud team watching for suspicious transactions can both be doing their jobs well and still miss the fact that they're looking at two stages of the same attack.
A shared IP address across seven firms is a useful piece of evidence precisely because somebody had the visibility to connect it. Device signals, identity intelligence, and behavioural patterns work the same way: individually suggestive, genuinely useful only once they're read together, and only once that reading happens across more than one institution's own four walls.
Level Five's Perspective
The attacker IPs rotated through eight countries to sustain one campaign against seven Korean financial firms. No single regulator, no single national CERT, no single institution's own security team had visibility into that full rotation. Each one saw a fragment, an IP here, a login attempt there, and the full pattern only became visible once someone compared notes across borders that rarely compare notes.
This is not a problem specific to Korea, it’s the default condition for any attacker sophisticated enough to spread infrastructure across jurisdictions on purpose, which is now most of them. A security framework built around one country's financial sector, however well-resourced, is answering a question scoped to a boundary the attacker never respected.
We see this gap from an unusual angle. Reselling platforms like Darwinium means watching, first-hand, where even strong device-identity-behaviour models hit their ceiling: the moment a pattern moves across institutions or borders faster than any single platform's validation cycle was built to track. That's exactly why we're building our own solution alongside the reselling work, not from a generic roadmap, but from watching where the tools we deploy run out of road.
So the question worth asking isn't whether your institution has good security. It's whether you'd have caught that same IP address on the third firm, or only found out when a regulator told you it was the seventh.
If you're thinking through what connected threat visibility would actually look like for your institution, feel free to reach out to Timmy Bang, our Korean Sales Director, or email us at marketing@levelfive.ai
Excited to learn more?
the Future of Secure, Compliant, and Connected Enterprises
